

Hackers Forced French Supermarket Fridges to Heat to 50C Overnight
Attackers forced Danfoss refrigeration systems at hundreds of French supermarkets into prolonged defrost overnight on 11-12 October 2026, spoiling food.

On this page
Key takeaways
- Attackers forced refrigeration systems at hundreds of French supermarkets into prolonged defrost overnight on 11 to 12 October 2026, heating some units to about 50°C for roughly six hours.
- The target was refrigeration management software from the Danish firm Danfoss; Danfoss said the affected units were legacy products, or current models running outdated firmware, that no longer receive software or security updates.
- Store counts come from the chains themselves: Intermarché and Netto reported about 180 stores hit, Coopérative U more than 100, Carrefour 80 of its 6,000, and Monoprix roughly 5% of its stores.
- The Paris prosecutor's office opened a cyber-crime investigation, and Prime Minister Sébastien Lecornu instructed the national cybersecurity agency ANSSI to investigate a vulnerability in Danfoss-supplied software.
- Ahold Delhaize reported a separate security issue that took Albert Heijn systems offline in the Netherlands; no link to the French attack has been established.
Overnight on 11 to 12 October 2026, attackers took remote control of the refrigeration systems at hundreds of French supermarkets and forced the units into prolonged defrost cycles. Some cabinets reached about 50°C (122°F) for roughly six hours, a figure Intermarché gave to AFP and The Guardian carried. Staff arriving for the morning shift found warm air coming off the freezers. A few stores had small fires. Fresh and frozen stock had to be thrown out.
Related reading: Leakers$ Hijacked Public LED Billboards in Egypt, Malaysia and Brazil · CISA Flags PolyShell as Exploited While the Magento Campaign Hits Hundreds of Stores.
BBC News reported the attack on 12 October, the same day the Paris prosecutor's office opened a criminal investigation. Danfoss, the Danish engineering company whose refrigeration management software runs the units, said the affected equipment was old. France's national cybersecurity agency is examining a vulnerability in that software, according to a source close to the prime minister.
What a forced defrost does
A refrigeration controller is a small computer that keeps a compressor, a fan and a defrost heater working in the right order. The defrost cycle melts the ice that builds on a freezer's coils. Under normal settings it runs for around two hours a day. The attackers overrode those limits and left it running, Tom's Hardware reported. BFM TV described a forced, continuous defrost with a setpoint of 50 degrees, the BBC noted.
That is why the damage was physical and fast. A defrost heater is built to warm coils, not a whole cabinet of milk and ice cream. Once the setpoint is raised and the cycle is not allowed to stop, the unit becomes a heater with a door on it. Intermarché said its fridges ran at 50°C for about six hours, and that everything in them was discarded.
The scale, on the chains' own numbers, is the largest part of the story. Intermarché and its Netto brand, both part of the Les Mousquetaires group, put the figure at about 180 stores, with a spokesman telling the BBC that another 100 shops were urgently disconnected from the internet to keep the same thing from happening to them. Coopérative U, which runs the Super U chain, said more than 100 of its stores were hit. Its chief executive, Dominique Schelcher, called the attack "extremely serious and unprecedented" in a post on X. Carrefour said 80 of its 6,000 French stores were affected. Monoprix reported trouble at roughly 5% of its more than 400 stores, and removed food from sale where it could not guarantee the cold chain. E.Leclerc and Auchan also reported incidents.
Add those up and the total sits near 400 stores, out of roughly 15,000 supermarkets in France. Every one of those figures is a chain's own count, and early reporting varied: Intermarché's number appeared as both 150 and 180 in the first day of coverage.
The target was old firmware
The common thread is Danfoss. The company sells the controllers and the software that let a retailer watch and adjust cold units across a chain, often from a central console. A source close to the investigation told AFP that Danfoss refrigeration control systems were the target.
Danfoss's own statement was careful. The company said it was "aware of incidents in France affecting a limited number of refrigeration management systems," and that the affected units "were running outdated firmware," according to The Guardian. CBS News reported that Danfoss told AFP most of the affected equipment was "legacy" product that "no longer receive[s] software or security updates," naming the AK-SM800 and AK-SC355 controllers as notably affected. The company said it had "long advised" customers to keep supported systems patched and to migrate away from legacy systems.
That framing puts the incident at the meeting point of two known problems. Legacy industrial controllers often sit on a network so they can be managed remotely, and once a vendor stops supporting them, the firmware they run does not change. A device that cannot be patched stays reachable, and stays vulnerable, for as long as it is plugged in.
An OT attack with a grocery bill
Most cyberattacks in the news take data. This one took temperature. The distinction matters because the systems involved are operational technology, the hardware that runs physical processes, rather than the office IT that stores records. An OT incident can be felt within hours, and the harm shows up as spoiled stock, damaged equipment and, in a few cases, fire.
The local numbers show how quickly that adds up. Cybernews reported that two supermarkets in Alsace, an Intermarché and a Super U in Haguenau, lost around €270,000 worth of goods between them, and that nationwide losses could run into the millions of euros. BFM TV showed a freezer in an ice-cream aisle reading 26.5°C, which is not a temperature any ice cream should sit at for long. Intermarché said it threw away all the affected food.
Food retail runs on thin margins and tight cold-chain tolerances, and the systems that hold the temperature are increasingly networked so a head office can manage energy use across hundreds of sites. That central control is what an attacker needs: one reachable console that sits in front of many stores.
The investigation, and who is not named
By the evening of 12 October, the case had moved to the state. The Paris prosecutor's office said it had opened an investigation into a "large-scale cyber-attack affecting the refrigerators of several major food retail chains across France," citing "food losses and fires," Reuters reported via U.S. News. Prime Minister Sébastien Lecornu instructed ANSSI, the national cybersecurity agency, to investigate, a person in his office said. The agency identified a vulnerability in Danfoss-supplied software, that source said.
No attacker has been identified, and no group has claimed the operation. That leaves the usual questions open. It is not known whether this was sabotage, an extortion attempt that has not yet surfaced, or a demonstration meant to be seen. Nothing in the public record answers them, and the first day of coverage produced no suspect and no motive.
The Ahold Delhaize thread, and why it is separate
The same weekend, the Dutch and Belgian retailer Ahold Delhaize reported a "security issue" of its own and took systems offline. Its Albert Heijn chain in the Netherlands saw its app and online delivery system go down, and electronic shelf labels displayed the wrong prices, NL Times reported. Delhaize stores in Belgium and Luxembourg were also affected, Grocery Dive noted.
It is tempting to read the two events as one campaign, and the timing invites it. The reporting does not support it. Ahold Delhaize described an IT outage with no mention of refrigeration, and no source has established a link between its systems and the French attack. The BBC said plainly that it was not clear whether the two were connected. Until someone shows the connection, they should be treated as separate.
What is confirmed, and what is not
The verified core is narrow and concrete. Hundreds of French supermarkets lost refrigeration overnight on 11 to 12 October 2026 after attackers forced defrost cycles. The software involved was Danfoss. The state opened an investigation. No one has been named.
Several details are weaker than they look. The 50°C figure comes from Intermarché, and Danfoss did not confirm the temperature. Store counts are figures the chains supplied, not an audited total, and Intermarché's own number moved between 150 and 180 in a single day of coverage. The ANSSI finding rests on a source close to the prime minister rather than a published advisory. The €270,000 loss for two Alsace stores is a local figure, not a national one.
Reported, not audited
The scale of the French refrigeration attack is a set of chain-supplied counts, not a finished tally. Intermarché's figure alone was reported as both 150 and 180 stores, Danfoss did not confirm the 50°C temperature, and ANSSI's vulnerability finding comes from a source close to the prime minister rather than a public advisory. Read every number here as a claim with a source attached.
Why food is a target
The reaction from Brussels was quick. European Food Commissioner Christophe Hansen condemned the attack and wrote on X that "food security requires more attention at all levels. Because the weaponisation of food has become a reality," Metro reported.
Food security requires more attention at all levels. Because the weaponisation of food has become a reality.
A cold chain is a form of stored trust. Shoppers assume the milk and the meat have been kept safe, and that assumption depends on equipment most of them never see. An attack that spoils food for a few hundred stores is disruptive. The same technique, aimed at a distribution centre or run for a longer window, would be a larger problem.
France said it was coordinating with European counterparts. Food retail now sits in the same security conversation as power grids and water systems.
What to watch
Whether the investigation names anyone, and whether it stays inside France. Attribution has been the slow part of nearly every major OT incident, and this one has no claim of responsibility to start from.
What Danfoss does with the controllers still in the field. The company's position is that it warned customers to migrate. The question regulators are likely to ask is what happens to the units whose owners did not, since those remain reachable and, on the company's own account, unpatched.
Whether the chain counts hold. If the confirmed total moves, so does the sense of how wide the campaign was. The first reports put it near 400 stores, and that figure is the sum of numbers each chain gave for itself.
And whether the two threads join. If investigators find a link between the French refrigeration attack and the Ahold Delhaize outage, the story becomes a coordinated cross-border operation against food retail. If they do not, it stays what it looks like now: two separate incidents with no proven connection.
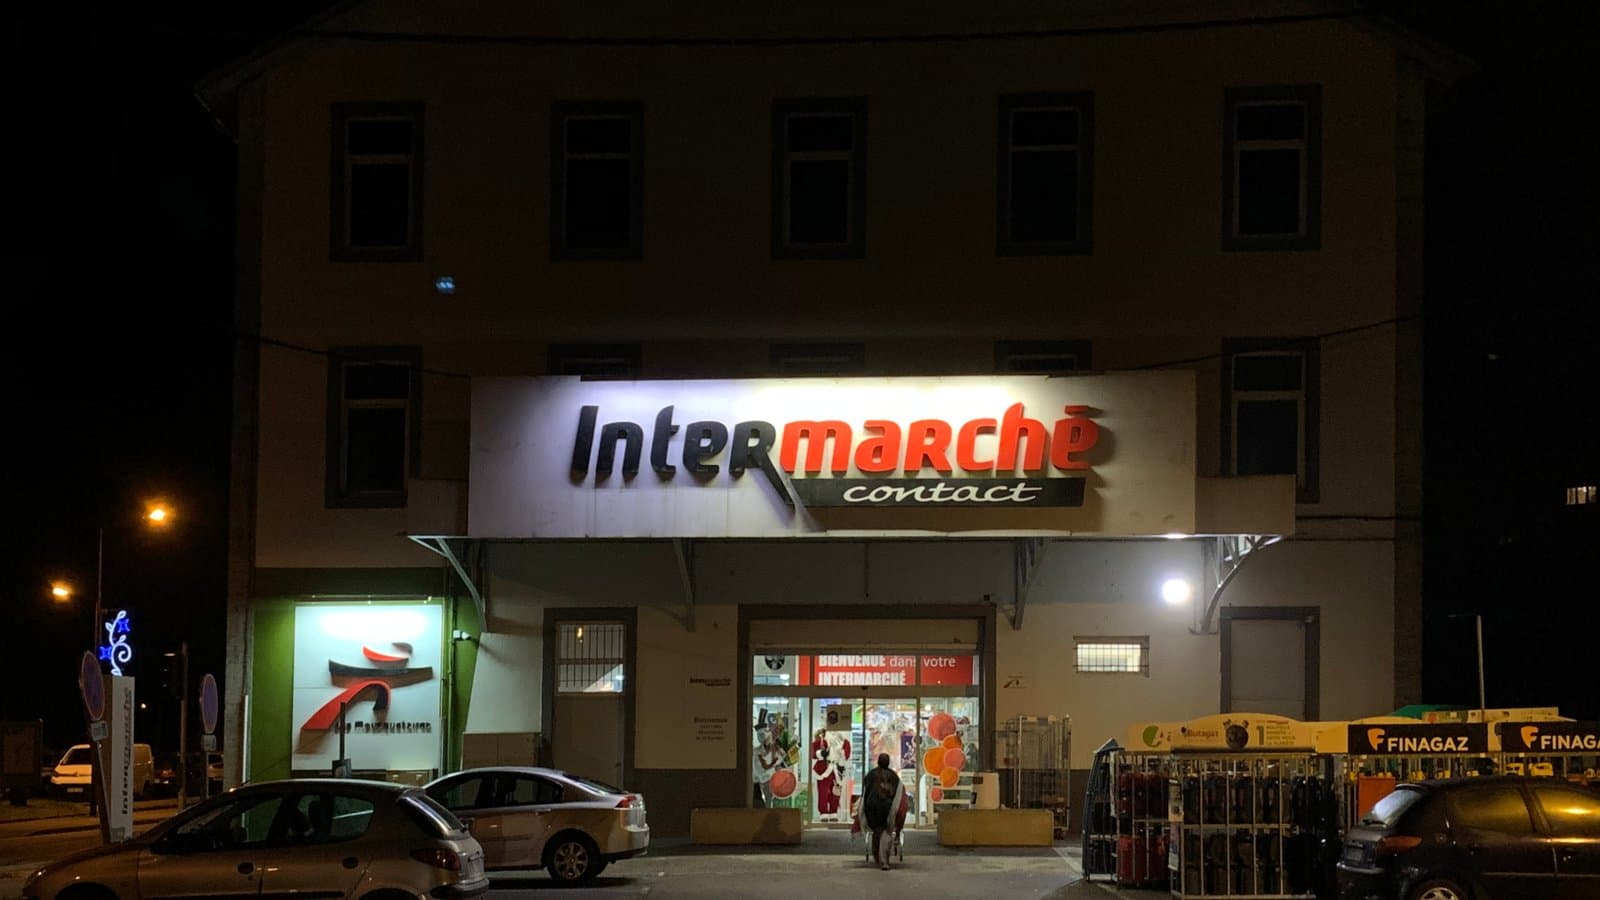
Cover image: "Intermarché Contact à Saint-Rambert-en-Bugey (décembre 2019).jpg" by Benoît Prieur, CC0, via Wikimedia Commons. An Intermarché store in France.
Tags
Frequently asked questions
- What happened to French supermarket fridges in October 2026?
- Overnight on 11 to 12 October 2026, attackers forced refrigeration units at hundreds of French supermarkets into continuous defrost cycles. Some fridges and freezers reached about 50°C for roughly six hours, spoiling fresh and frozen food. Intermarché said it threw away all of the affected stock, and a few stores reported small fires.
- Which supermarkets were affected by the refrigeration cyberattack?
- The named chains are Intermarché and its Netto brand (about 180 stores, per the company), Coopérative U's Super U (more than 100), Carrefour (80 of 6,000), and Monoprix (roughly 5% of its stores). E.Leclerc and Auchan also reported incidents. The counts are figures the chains supplied, not an audited national total, which early reports put near 400 stores.
- How did the attack heat supermarket fridges to 50C?
- The attackers overrode the normal defrost limits on Danfoss refrigeration controllers and kept the cycle running. A defrost cycle is meant to run for around two hours a day to melt ice off a freezer's coils; the attackers set a 50°C target and let it run for hours. Intermarché gave the 50°C and six-hour figures, and Danfoss did not confirm the temperature.
- Is the Ahold Delhaize outage linked to the French supermarket attack?
- No link has been established. Ahold Delhaize reported a separate security issue that took Albert Heijn's app and online ordering offline in the Netherlands, with Delhaize stores in Belgium and Luxembourg also affected. The company described an IT outage with no mention of refrigeration, and no source has connected it to the French attack.

TPW Editorial
Editorial Team
TechPastWeek's editorial team reports and edits every story we publish. We research each piece against primary and credible secondary sources, and a human editor reviews and signs off before it goes live.





