

Apple Warned German Lawmakers of Mercenary Spyware. Germany Cannot Say If It Worked
Multiple Bundestag members received Apple threat notifications for mercenary spyware. Germany's BSI says it cannot tell a real compromise from an attempt.

On this page
Key takeaways
- Germany's federal cybersecurity office (BSI) said in a notice published over the weekend of 31 October to 1 November 2026 that multiple Bundestag members and other public figures had received Apple threat notifications since 29 October 2026.
- The BSI said it does not know whether the notifications indicate actual compromises or only attempted attacks, and advised recipients to assume their device may be compromised.
- The BSI sent a letter to Bundestag members on 30 October 2026, one day after Apple's notifications began arriving, to raise awareness and set out protective measures.
- Apple says threat notifications are high-confidence warnings that a person was individually targeted, but the alert does not say whether an attack succeeded, and Apple does not attribute attacks to governments.
- Beirut-based filmmaker Radwan Mortada said his notification stated Apple's latest batch went to users in 99 countries, a figure neither Apple nor the BSI has published for this round.
Germany’s federal cybersecurity office says multiple members of the Bundestag received warnings from Apple that their iPhones may have been targeted with mercenary spyware. The BSI said in a notice published over the weekend of 31 October to 1 November 2026 that the notifications had been arriving since 29 October, and that other public figures had received them too. It does not know whether any of those phones were compromised.
Related reading: FBI Arrests OpenAI Employee Accused of Planting a Hidden Recording Device · Microsoft's October 2026 Patch Tuesday Sets a Record With 1,407 Fixes.
The BSI sent a letter to members of parliament on 30 October, a day after the notifications began, to raise awareness and set out what recipients should do. Apple’s message was direct: it had detected an attack using mercenary spyware, the commercially developed surveillance software that has historically been used against a small number of specifically chosen people.
Two things are missing from the public record. There is no confirmed victim and no count of affected devices. The question a reader will ask first, whether these phones were hacked, has no answer yet.
The BSI confirmed the warnings, not the hacks
The notice is carefully worded, and the caution looks deliberate. The BSI does not know whether the notifications mean actual compromises or merely point to attempted attacks, it says. Recipients should assume their device may have been compromised.
That is not a contradiction. A threat notification is a signal about targeting: Apple has high confidence that someone aimed at this person. It is not a report on whether the attack worked. Apple builds these alerts from its own threat-intelligence work, and the company says its investigations can never reach absolute certainty.
The BSI notice does not name the victims or say how many members of parliament were affected. The letter of 30 October went to members of the Bundestag as a group, so receiving it is not the same as receiving an Apple alert.
Berlin has said little beyond confirming that it is paying attention. Government spokesperson Stefan Kornelius said the government was “taking the incident and the warning very seriously,” according to the Financial Times. He did not say who in the federal government had been targeted, including whether Chancellor Friedrich Merz was among them.
How zero-click spyware gets onto a phone
The term in Apple’s notification is “mercenary spyware,” and it covers a category of commercial intrusion tools sold to governments and other well-funded buyers. These tools are built for a handful of specific people, and they do not spread across the internet. Apple says such attacks cost millions of dollars and often have a short shelf life, which is part of why they are hard to detect.
The delivery method that matters here is the zero-click exploit. A crafted message arrives and does the work without the recipient opening it, tapping a link or installing anything. There may be nothing to see: no obvious app, no strange icon, no prompt to approve. The BSI says infected devices are usually not noticed by their owners at all, though it lists frequent crashes and fast battery drain as possible signs worth taking seriously.
Once a phone is compromised, the list of what an attacker can reach is long. The BSI names messages, including those inside encrypted messenger services, plus calls, contacts, calendar entries and location. The camera and microphone are in scope too. End-to-end encryption protects a message while it travels between two phones. It does not help when the phone at one end is recording what the user sees before the message is ever encrypted.
A high-confidence warning still leaves the outcome open
The alert is easiest to misread by collapsing three states into one. A notification means Apple has high confidence that a person was individually targeted. It does not mean the attack succeeded, it does not identify the attacker, and it does not say which message, service or vulnerability was involved.
Apple’s support page puts the confidence claim plainly: threat notifications are “high-confidence alerts that a user has been individually targeted by a mercenary spyware attack, and should be taken very seriously.” The same page explains why Apple will not say more. Revealing what triggered a notification could help attackers adapt their tools and avoid detection next time.
Three states, one alert
A notification can sit on top of an attempt that was blocked or failed, an attempt that succeeded, or, rarely, a warning that later turns out to be wrong. Apple says its alerts are reliable, but also that its investigations cannot be certain. The BSI’s advice to assume compromise follows from the middle option, which nobody can currently rule out.
There is a second trap, and it is mundane: fake threat notifications exist, and they are phishing. Apple says a genuine notification never asks the user to click a link, open a file, install an app or profile, or give up an Apple Account password or verification code. Anyone unsure whether an alert is real can sign in to account.apple.com directly; a real notification appears at the top of the page. The BSI adds that genuine alerts also appear on the lock screen, in Settings, and by email to the addresses on the account.
The political stakes Berlin has not addressed
Members of a national parliament sit on committees that see draft legislation, budget papers and closed-door briefings before any of it becomes public. They talk to ministers, foreign officials and constituents who bring problems they cannot take anywhere else. A compromised phone in that setting is a window into conversations that never appear in a press release.
So the guidance is addressed to individuals. A national cyber agency issued advice for members of parliament, pointed them to its service centre, and asked recipients to report so it can judge the scale. The agency has not said what it will do with those reports, or whether they will feed a formal investigation.
The gap between the warning and the public account has not narrowed. Germany has confirmed that warnings went out and that it takes them seriously. It has not confirmed a single compromised device, named a suspect, or described how a compromise would be established.
Germany’s own history with the same tool class
Germany’s Federal Criminal Police Office, the BKA, reportedly acquired access to NSO Group’s Pegasus spyware in 2019, as DW reported. Nothing in the BSI notice or in the reporting suggests the BKA or Pegasus is involved in the current warnings.
That purchase does not connect to this case, but it complicates the political response. A government whose own federal police reportedly bought access to such a tool now has to respond to its apparent use against its legislators.
The 99-country figure and the attribution gap
Germany was not the only country affected. Radwan Mortada, a Beirut-based filmmaker, said on X that he received a new Apple notification warning of “another attack against your device,” after an earlier spyware attack in 2021. His notice said Apple’s latest batch went to users in 99 countries, TechCrunch reported.
That number comes from one recipient’s account of one message. Neither Apple nor the BSI has published a count for this round. Apple says it has sent threat notifications multiple times a year since 2021 and has notified users in more than 150 countries in total.
Who is behind the campaign is unknown. Apple says it does not attribute attacks or notifications to specific attackers or regions, and the BSI notice names no government, vendor or suspect. The market Apple describes involves private companies developing spyware for state clients. Which company, if any, supplied the tool used here has not been made public.
What the BSI tells recipients to do
The guidance is more specific than the public debate around it. The first instruction carries a condition that matters: update the operating system immediately, unless a forensic analysis is planned. Patching a phone can destroy the traces an investigator would need, so the decision to preserve evidence has to come before the update, not after. For most people the answer is still to update.
- Enable Lockdown Mode and keep it on. On an iPhone: Settings > Privacy & Security > Lockdown Mode. The BSI says to leave it enabled permanently, including on a replacement device. It restricts some features, among them message attachments, link previews and FaceTime calls from unknown callers; ordinary calls and text messages keep working. It makes new attacks harder. It does not remove an infection that is already there.
- Replace the device if the risk is judged high. The BSI pairs that with resetting every account used on the phone and changing the phone number, a significant step for anyone whose number is also a political and professional contact point.
- Set a new device passcode that differs from the old one. Face ID and Touch ID do not replace it.
- Change passwords for the Apple Account, email accounts and any other account used on the device, turn on two-factor authentication where it is missing, and add a new trusted phone number before removing the old one. Authenticator apps should be set up again at each service instead of being transferred from the old phone.
- Lock down the messengers. Signal has a registration lock; WhatsApp has two-step verification. Both should be enabled with a new PIN or password, and linked devices reviewed, with anything unrecognised removed. The same check applies to the device list on the Apple Account.
- Report the notification to the BSI’s service centre at [email protected], which the agency says helps it assess the scale.
Replacing a phone and a phone number disrupts years of contacts and two-factor setups, and for a member of parliament the number is part of the job. Updating immediately protects the device but may erase the evidence that would answer the question everyone is asking. The BSI’s conditional phrasing acknowledges that trade-off without pretending it can be settled for everyone.
Caveats: what remains unknown
A threat notification is not proof of a successful hack. The BSI says so itself, in the same notice that advises recipients to assume the worst. Both statements can be true: the agency cannot rule out a compromise, and it cannot confirm one.
The count is unknown. “Multiple” is the BSI’s word for the number of Bundestag members affected, and the agency has not put a figure on it. The names are unknown; the government has refused to say whether the chancellor is among them. The 99-country figure is second-hand. The cause is unattributed.
One gap is unlikely to close quickly. Mercenary spyware is built to leave little trace, and a phone that has been updated, reset or replaced may never yield a clean answer. No forensic findings have been published, and no one has shown that these devices were clean.
What to watch
The first signal is whether the BSI moves from guidance to findings. A count of reported notifications, a confirmed infection, or a statement that forensic analysis found nothing would each change the story. The agency has not said which it expects.
The second is the Bundestag. Parliament will have to decide whether anything about members’ devices or communications should change. A concrete change to device policy or secure-communications advice would matter more than another statement of concern.
The third is attribution. Apple’s page notes that public reporting and research by civil-society groups, technology firms and journalists have documented commercial spyware campaigns before. None has published findings on this batch, and any link to a specific customer, country or vendor would take time to establish.
As of 3 November, the BSI had published guidance, not findings.
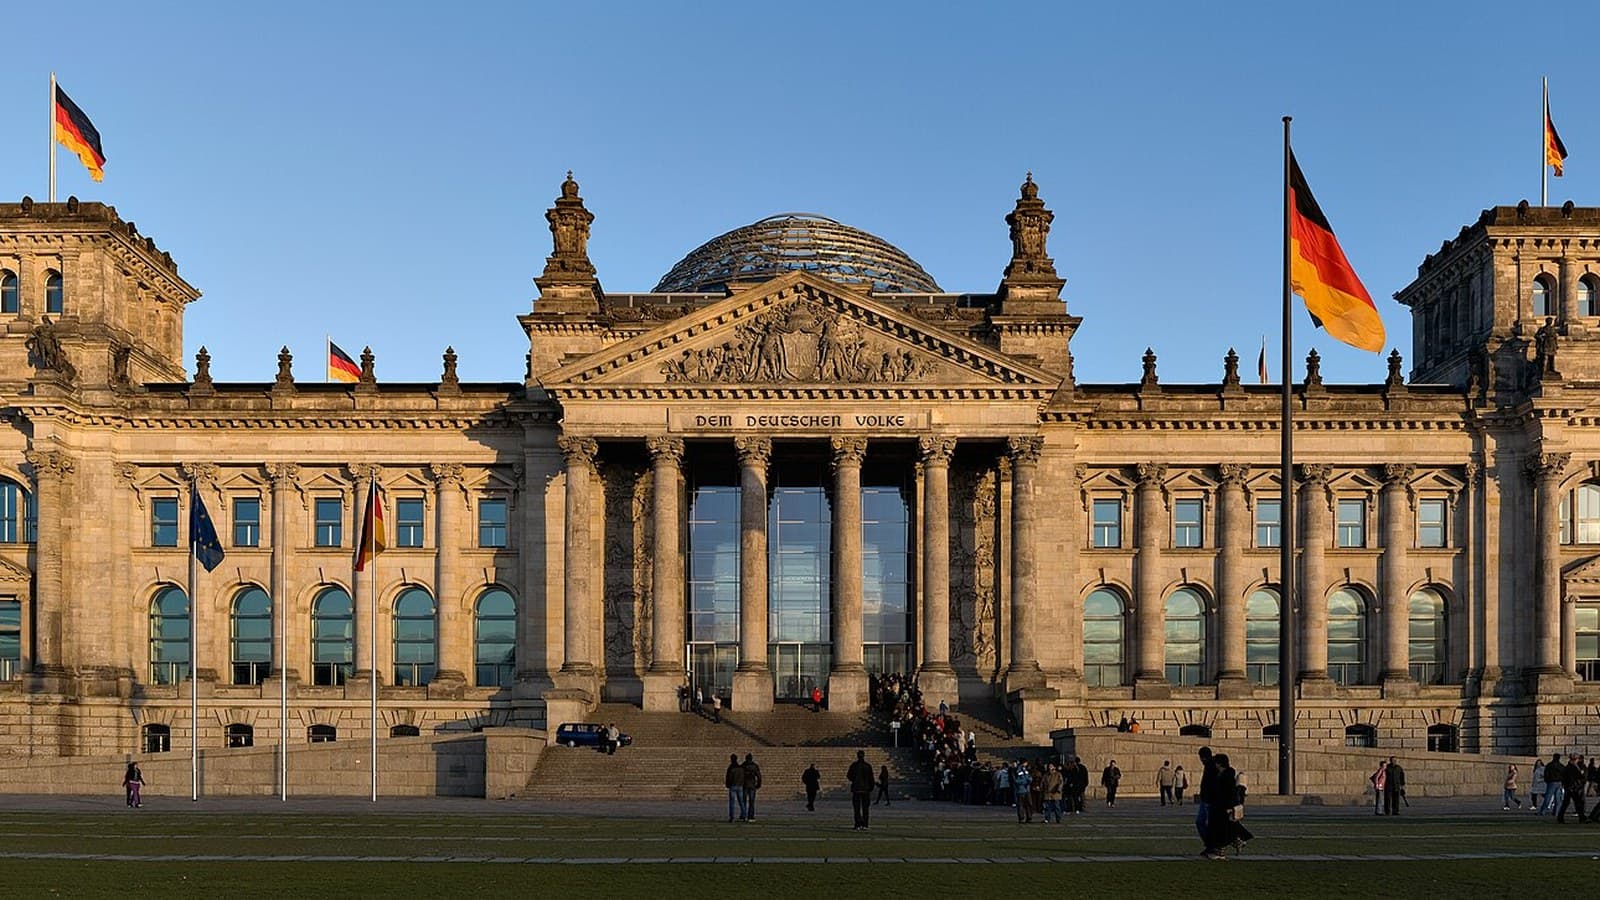
Cover image: "Reichstag building Berlin view from west before sunset" by Jürgen Matern, CC BY-SA 3.0, via Wikimedia Commons, cropped 16:9.
Tags
Frequently asked questions
- Were German lawmakers' iPhones actually hacked?
- Nobody has confirmed that. The BSI said it does not know whether the Apple notifications mean actual compromises or only attempted attacks, and it advised recipients to assume their device may have been compromised. No forensic findings have been published.
- What is zero-click spyware?
- It is spyware that infects a device without the user doing anything, often through a crafted message that does not need to be opened. The BSI says victims usually notice nothing, and an infection can expose messages, calls, contacts, calendar, location, camera and microphone.
- Who is behind the attacks on German lawmakers?
- That is unknown. Neither Apple nor the BSI has attributed this campaign to a government or a spyware vendor, and the BSI notice does not name any suspect. Apple says it does not attribute threat notifications to specific attackers or regions.
- What should I do if I receive an Apple threat notification?
- The BSI advises updating the operating system immediately unless a forensic analysis is planned, enabling Lockdown Mode permanently, and changing the passcode and the passwords for accounts used on the device. Recipients should also report the notification to the BSI's service centre.

TPW Editorial
Editorial Team
TechPastWeek's editorial team reports and edits every story we publish. We research each piece against primary and credible secondary sources, and a human editor reviews and signs off before it goes live.





