

‘LLM-Jacking’: Hijacked AI Accounts Are Fueling a New Cybercrime Boom
Security researchers warn LLM-jacking is surging, as attackers steal AI credentials and resell cheap access to costly models, feeding a fast-growing market.

On this page
Key takeaways
- A Financial Times investigation published on September 26, 2026 reported a surge in ‘LLM-jacking,’ in which attackers steal cloud and AI credentials to run or resell access to costly large language models.
- Google Threat Intelligence Group said underground prices for AI accounts more than doubled in 2026, and the FT reported dark-web access to Anthropic, Google and OpenAI models selling at discounts of up to 97 per cent.
- The FBI's Internet Crime Complaint Center logged 22,364 AI-related complaints in 2025, the first year it tracked the category, with reported losses of nearly $893 million.
- Security firm Gambit documented one campaign in which autonomous AI agents stole more than 600,000 credit-card records from two online retailers and hit at least 119 sites with skimmers, at about $25 per scanned target.
- Sysdig's Threat Research Team coined the term LLMjacking in May 2024 after finding stolen cloud credentials used to run hosted model services, and estimated worst-case costs above $46,000 per day.
On September 26, 2026, the Financial Times published an investigation reporting that security researchers have warned of a surge in "LLM-jacking," a class of attack in which criminals steal cloud and AI credentials to run or resell access to costly large language models at someone else's expense. The piece, by Tom Wilson, describes illicit access to AI models and computing power as fast becoming "the hottest commodity in the cyber criminal underworld."
Related reading: Dutch Police Arrest Alleged ShinyHunters Leader as FBI Breach Fallout Grows · Leakers$ Hijacked Public LED Billboards in Egypt, Malaysia and Brazil.
John Hultquist, chief analyst for Google Threat Intelligence Group, told the FT that his unit had seen a major increase in LLM-jacking this year, including the sale of stolen login credentials for public AI tools and the theft of computing resources by groups that want to run their own models for free.
"What we are seeing in the underground is a growing economy associated with access to AI," Hultquist, a 20-year cyber security veteran, told the FT. Cheap access to expensive models, he said, gives attackers a financial edge over the companies that must use the same tools to defend themselves. "The bottom line is all this behaviour gives them a sort of economic or efficiency advantage against us, because they're going to essentially be able to get their hands on these tokens at a much cheaper rate," he said.
What LLM-jacking is
The mechanics are simple, and that is what makes the attack attractive. Enterprise AI agents and applications authenticate to a model with an API key or a session token, a string that often carries the full spending power of a company's account. If an attacker obtains that string, they can call the same models the company pays for and leave the bill with the victim.
The attack got its name in May 2024 from the Sysdig Threat Research Team, which said it coined the term "LLMjacking" after observing stolen cloud credentials used to target ten cloud-hosted model services. The credentials in that case came from a system running a vulnerable version of Laravel tracked as CVE-2021-3129. Sysdig found evidence of an LLM reverse proxy, software that lets an operator resell access to a pool of compromised accounts while hiding the underlying keys.
Sysdig estimated that a single abused Anthropic Claude 2.x account could generate more than $46,000 in inference costs per day. A later Cloud Security Alliance research note put attacks targeting Claude 3 Opus above $100,000 per day.
Why AI accounts are worth stealing
The most advanced ChatGPT and Claude subscriptions can cost as much as $200 per user a month, and the FT, citing Google Threat researchers, reported that dark-web marketplaces sell access to models from Anthropic, Google and OpenAI at discounts of up to 97 per cent. As more companies host or buy expensive AI capacity, the account itself becomes the prize.
Google's threat intelligence group said in a September 8, 2026 report that underground demand for AI accounts rose through the year, concentrating on Claude and Gemini credentials, with average marketplace prices per account more than doubling in 2026. Demand also stretched to autonomous coding tools such as Cursor Pro and Devin.
The trade is not new. eSentire's Threat Response Unit reported in July 2024 that criminals were selling roughly 400 individual GenAI accounts a day, with OpenAI credentials the most common at about 200 posted daily. Stealer logs went for about $10 each, and stolen GPT-4 or Claude API keys were advertised at around $15, the firm said.
Competition among sellers has changed the offer. Because AI labs watch for abuse and disable compromised accounts, some sellers now market "guaranteed access," Hultquist said, committing to provide replacement credentials at no extra cost if the first account is blocked.
A template for cheap AI-enabled crime
LLM-jacking is about stealing model access, but a parallel campaign shows how far the cost of AI-driven intrusion has fallen. Gambit Security reported on September 22, 2026 that a financially motivated operator, described by researchers as Chinese-speaking, used three open-source AI harnesses to attack hundreds of online retailers. The tools were Strix for vulnerability scanning, Cairn for autonomous exploitation and Hermes for orchestration.
The campaign began in July 2026 and was still running in late September. BleepingComputer reported that the operator stole more than 600,000 valid credit-card records from two companies, including 488,372 belonging to U.S. cardholders, and placed payment skimmers on at least 119 sites. Gambit estimated the whole operation cost between $12,000 and $18,000, a mean of $25.46 across 101 completed scans. Where access was achieved, it usually took under a day.
That campaign is a case of AI-enabled crime rather than stolen model access, but the two share a driver: the marginal cost of an AI-assisted attack has dropped into the tens of dollars, which removes cost as a filter on who can attempt one.
How the credentials leak
Anthropic's September 2026 threat intelligence report describes a mature criminal supply chain built around AI access. It says access in the form of compromised API keys, session tokens and devices "has increasingly become the sole objective of multiple criminal groups," which then sell that access through brokers that feed fraudulent AI reseller networks.
The report argues that operators who obtain AI credentials gain three things at once. It labels them "Loot," meaning resale value in established markets; "Compute," meaning attack workloads that run at someone else's expense; and "Cover," because the activity is attributed to the credential's legitimate owner. Anthropic describes ShinyHunters affiliates who, after stealing a victim's AI keys, switched their own attack workloads onto the victim's keys, and a hacktivist campaign that ran for a month entirely on stolen API keys.
Google's threat intelligence team traced much of the supply to infostealer malware, naming Lumma, Stealc, Vidar and ACRStealer. In May 2026, it said, ACRStealer controllers pushed file-grabber rules at the configuration stores of AI coding assistants, targeting the secrets.json file of Cline and the config.yaml file of Continue. Those files can hold plaintext API keys and custom model endpoints. In a separate case in April 2026, Mandiant responded to an intrusion in which an exposed GitHub personal access token let an attacker stand up unauthorized AI infrastructure and request quota increases for GPUs.
How big the problem has become
Public data is thin, and much of what exists comes from vendors that also sell defenses. The clearest official figure comes from the FBI. Its Internet Crime Complaint Center logged 22,364 complaints carrying an AI-related descriptor in 2025, the first year it tracked the category, with reported losses of nearly $893 million.
Private estimates run higher. CTech, the tech arm of the Israeli outlet Calcalist, reported in August 2026 that LLM hijacking had already caused an estimated $1 billion in cumulative organizational losses that year. Dima Tatur, vice president of cyber defense at the security firm Commit, told CTech that "the losses are averaging $50,000 to $100,000 per day per company affected."
Anthropic said its threat intelligence team disrupted malicious use of Claude across more than two dozen countries, including the United States, Britain and Yemen, in the eight months to August 2026, according to the FT.
What companies should do
The defensive advice converges on treating AI credentials with the same seriousness as production secrets. Anthropic's report states plainly that AI access should be bought only through authorized channels, because a discount that requires routing credentials through an unknown intermediary exposes data and systems to the middleman.
Several practical controls follow from the research:
- Give API keys short lifetimes, scope them to least privilege and rotate them on a schedule. Sysdig's original write-up recommends secrets management and entitlement management so that an abused account holds the minimum access it needs.
- Scan code, containers and public repositories for exposed keys, and watch AI developer configuration files in particular, since that is where Google says stealers now look.
- Monitor model invocation logs and spending. Hultquist told the FT that the best moment for attackers to blend in is now, while companies are still learning how much AI they use. "You might think a sudden major increase in compute usage is completely normal because you have just adopted all this AI infrastructure," he said. "It's a real opportunity for somebody to hide in the noise."
- eSentire recommends passkeys and FIDO2 security keys where AI platforms support them, plus dark-web monitoring to catch stolen credentials when they are advertised.
Tatur of Commit offered a three-step incident response: block the compromised key and cap consumption immediately; move the replacement key into a secure vault rather than pasting it back into source code, which is how repeat theft happens; then investigate the intrusion and ask the model provider for a credit. He warned that companies often struggle to reach the labs, describing communication as limited.
Caveats
A few boundaries are worth stating. The underground price and demand figures come from threat-intelligence vendors that also sell security products, so they should be read as informed estimates rather than audited accounts. The IC3 figure counts complaints with an AI descriptor attached, which is not the same as confirmed LLM-jacking incidents. The $1 billion loss estimate and the daily per-company losses are private calculations. And the FT's central voice is Google's Hultquist, whose employer competes in the security market it is describing.
What is not in dispute is the direction. The FT piece, Anthropic's disclosures, Google's tracker and independent incident reporting all describe the same shift: AI access has become a commodity worth stealing, and the cost of a credential is far below the damage a stolen one can do.
What to watch
Insurance could set the effective price of the risk. In April 2026, the FT reported that QBE and Beazley were drafting policy language to cap AI-related losses, with QBE applying sublimits to LLM-jacking events, so that a policy covering up to $5 million would pay only about $250,000 for those claims. Whether more insurers adopt similar caps will shape how much of the bill companies end up carrying themselves.
Keep an eye, too, on whether the AI labs improve the accounting and credit processes that victims currently find opaque, and on how quickly stolen AI accounts keep turning up in the intrusions that security teams investigate next. Hultquist's closing warning to the FT was blunt: "Anybody who decides that AI is a fad and wants to let it just wash over them is going to wake up one day underwater. They're going to have more incidents, more alerts, more attacks than they've ever seen before."
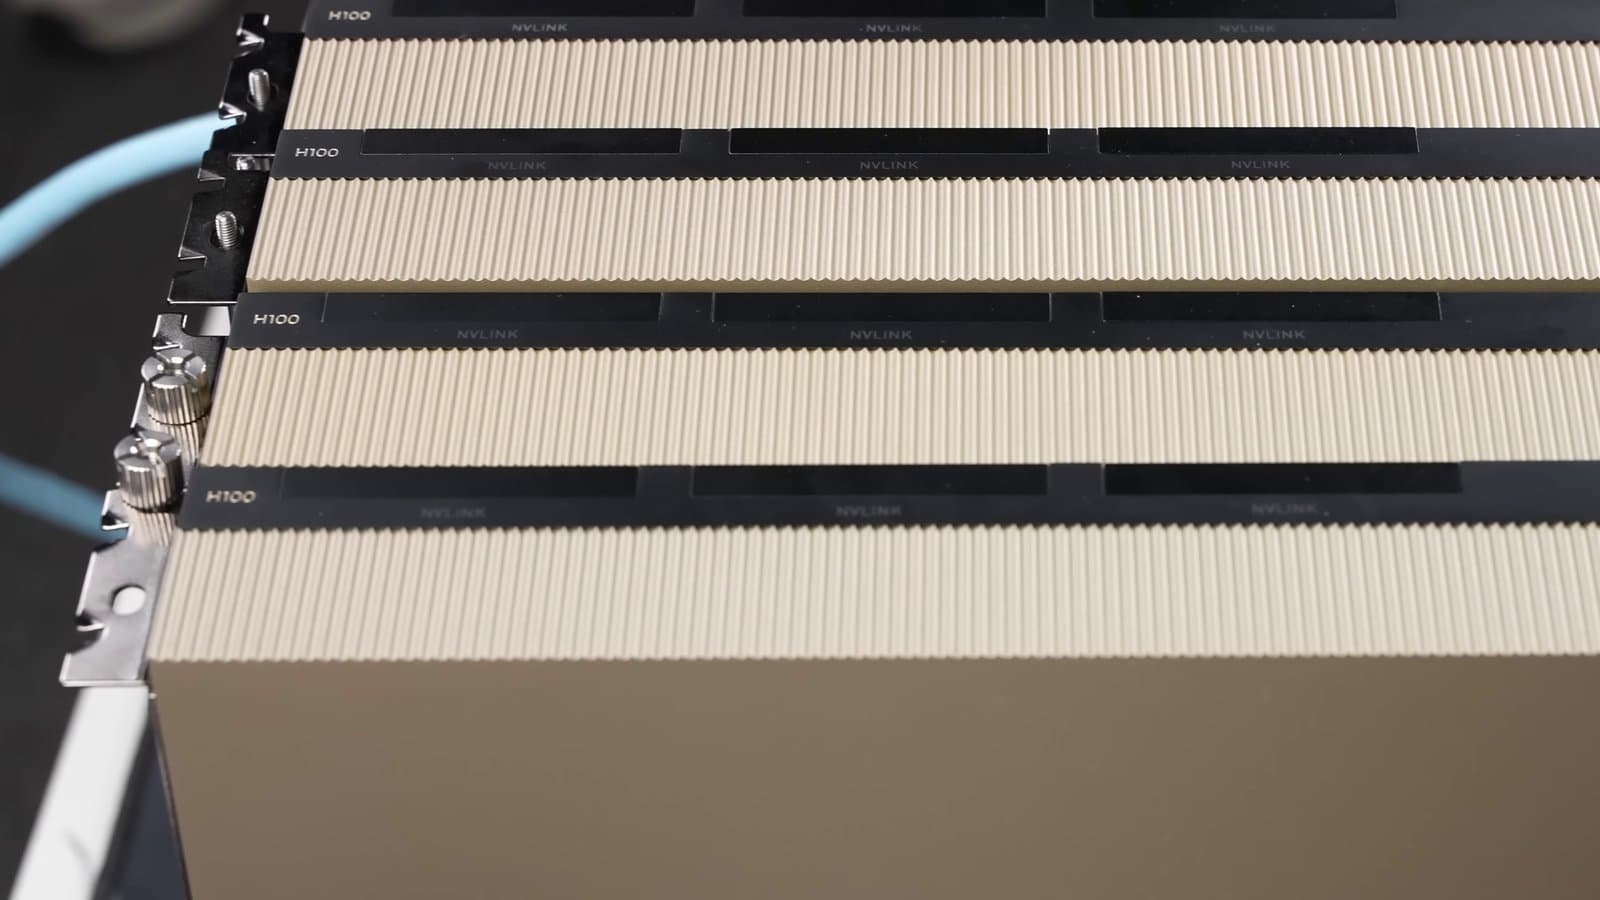
Cover image: NVIDIA H100 accelerators in a server. Photo by Geekerwan via Wikimedia Commons (CC BY 3.0).
Tags
Frequently asked questions
- What is LLM-jacking?
- LLM-jacking is the theft and misuse of access to large language models. Attackers obtain a company's API key or session token, then use the victim's paid model quota to run their own workloads or resell cheap access to other criminals, leaving the account holder with the bill.
- How much can a hijacked AI account cost a company?
- Sysdig estimated a worst case above $46,000 per day for an abused Claude 2.x account, and a later Cloud Security Alliance note put Claude 3 Opus attacks above $100,000 per day. Dima Tatur of Commit told CTech that affected firms averaged $50,000 to $100,000 per day.
- How do attackers get AI credentials?
- Google's threat intelligence team points to infostealer malware, exposed keys in public code and apps, and session tokens lifted from developer machines. Research firm eSentire found criminals selling hundreds of GenAI accounts a day on underground markets.
- What should companies do to stop LLM-jacking?
- Anthropic advises treating AI keys and agent integrations as production credentials and buying AI access only through authorized channels. Practical steps include short-lived keys, secret scanning, least-privilege scopes, spend alerts on model usage, and monitoring invocation logs for sudden spikes.

TPW Editorial
Editorial Team
TechPastWeek's editorial team reports and edits every story we publish. We research each piece against primary and credible secondary sources, and a human editor reviews and signs off before it goes live.





